
Why Small Businesses Are Actually Bigger Targets for Ransomware Than the Fortune 500
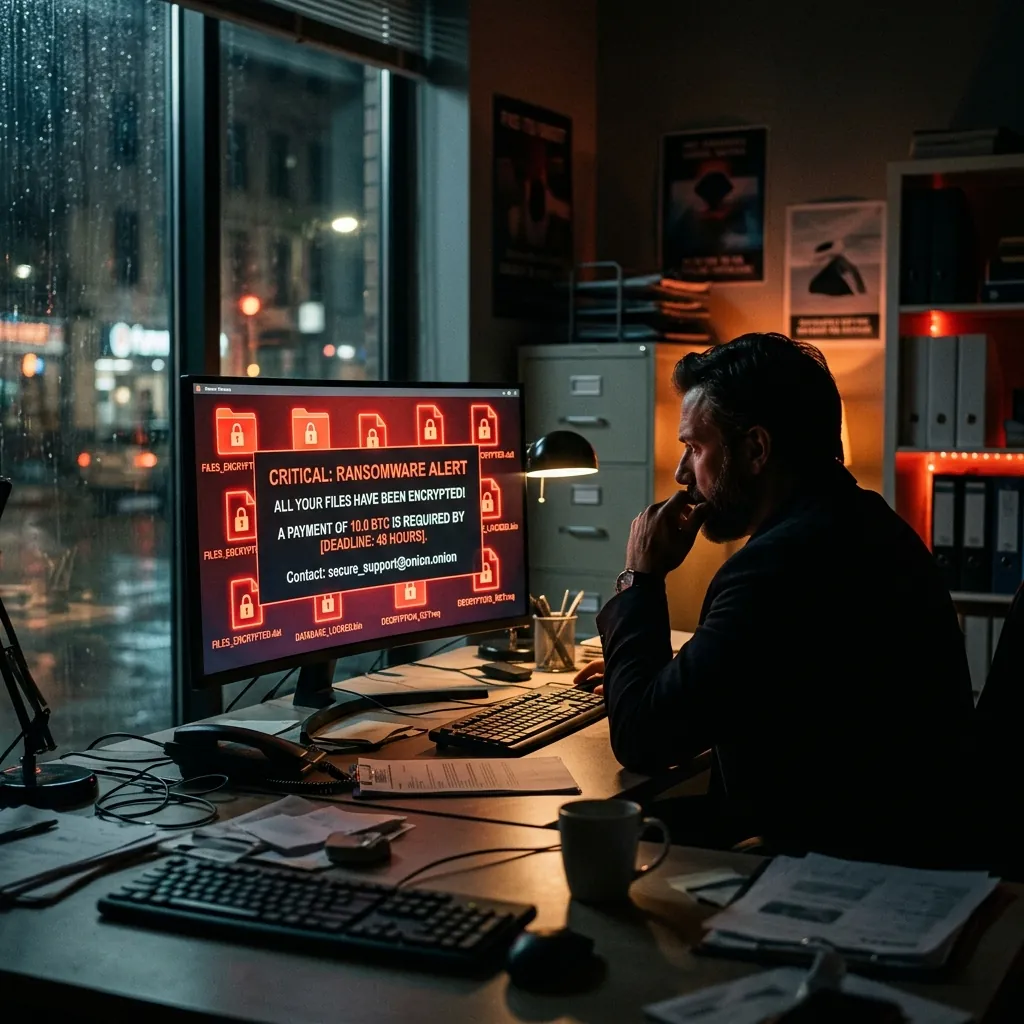
Think you're too small to be a ransomware target? The data says otherwise. Small businesses are hit by cyberattacks far more often than large enterprises—and the reasons why may surprise you.
There's a belief that persists in nearly every small business owner's mind: "Why would a hacker bother with us? We're not a bank. We're not a hospital. We don't have millions of dollars. They want the big fish."
It's an understandable assumption—and it is almost completely wrong.
The data tells a very different story. Small and mid-sized businesses (SMBs) are not afterthoughts in the ransomware economy. They are the primary target. Understanding why that's true—and what to do about it—could be the difference between an unfortunate near-miss and your business permanently closing its doors.
The "Too Small to Target" Myth: What the Numbers Actually Show
Let's start with the facts.
- 43% of all cyberattacks target small businesses, according to Verizon's annual Data Breach Investigations Report.
- 60% of small businesses that suffer a significant cyberattack close within six months, according to the U.S. National Cyber Security Alliance.
- The average cost of a ransomware attack on a small business is now over $200,000—a figure that includes downtime, recovery, ransom payments, and reputational loss.
- 82% of ransomware attacks in 2023 targeted companies with fewer than 1,000 employees, per the Coveware Quarterly Ransomware Report.
Hackers are not fishing for whales. They are running nets—and small businesses fill those nets.
Why Small Businesses Are the Preferred Target
This isn't random. Cybercriminals are rational economic actors. They attack where the payoff is highest relative to the effort required. Small businesses tick every box.
1. Weak or Nonexistent Security Infrastructure
Large enterprises employ dedicated security operations centers (SOCs), Chief Information Security Officers (CISOs), next-generation firewalls, 24/7 monitoring platforms, and sometimes entire teams whose sole job is threat hunting. They have the resources to make an attack genuinely difficult.
Most small businesses have none of that. They run on consumer-grade routers, Windows Defender, and the hope that nothing bad happens. For an attacker, this is the equivalent of a locked house versus an unlocked car.
The barrier to entry is simply much lower.
2. Employees Are Undertrained and Under-Warned
Phishing emails remain the single most common entry point for ransomware—accounting for 91% of all cyberattacks, according to Deloitte. Large organizations invest heavily in security awareness training, simulated phishing campaigns, and strict email filtering policies.
Small businesses often assume their employees just "know not to click on bad links." They don't. Not reliably. Not without consistent, repeated training. A single employee clicking the wrong email on a Tuesday morning is all it takes.
3. No Incident Response Plan
If a ransomware attack hits a Fortune 500 company, a trained response team is mobilized within minutes. Affected systems are isolated. Legal, PR, and executive stakeholders are notified simultaneously. The damage is contained.
If a ransomware attack hits most small businesses, the response is panic. Employees call each other. Nobody is sure who to contact. Critical time passes while the malware silently spreads from one machine to the next across the shared network. By the time anyone acts, the damage is done.
The absence of an incident response plan turns a survivable event into a catastrophic one.
4. Backups Are Either Missing or Vulnerable
The single most effective defense against ransomware—after preventing an infection in the first place—is having immutable, offline backups that the ransomware cannot reach and encrypt.
Many small businesses believe they have this covered because they use Microsoft 365 or have a drive plugged into a server. Both assumptions are dangerous. Microsoft's native data retention is not a backup solution. A network-connected drive can be encrypted just as easily as any other file. True ransomware-resilient backups require offsite, air-gapped, or immutable cloud storage that an attacker cannot access—even with valid credentials.
5. Small Businesses Are the Back Door Into Larger Ones
Here is an attack vector that rarely gets discussed: supply chain attacks.
Your mid-market or enterprise clients require you to be connected to their systems—their portals, their shared drives, their email threads. Attackers know this. Compromising your small business is often the path of least resistance to accessing a much larger organization.
This means you are not just protecting yourself—you may be contractually obligated to protect your clients. Many enterprise vendor agreements and cyber insurance policies now carry explicit data security requirements that your MSA likely references.
What Ransomware Groups Are Actually Doing
Modern ransomware gangs are not hackers in the Hollywood sense—lone geniuses hunched over keyboards. They are organized criminal enterprises operating ransomware-as-a-service (RaaS) platforms.
In a RaaS model, developers build and maintain the ransomware toolkits. Affiliates—who can be relatively unskilled—pay a subscription or revenue share to deploy the ransomware against targets of their choosing. These affiliates are specifically coached to target SMBs because:
- The ransom demands are calibrated to be "affordable." A $25,000–$75,000 ransom is below most small businesses' cyber insurance deductible—making it tempting to simply pay rather than fight.
- Recovery without backups is nearly impossible, creating maximum leverage.
- SMBs are unlikely to involve law enforcement, fearing publicity.
- Attacks can be automated at scale—scanning the internet for known vulnerabilities in unpatched routers, VPNs, and remote desktop protocols (RDP) is trivial with the right tools.
You are not being targeted by a mastermind with a grudge. You are being processed by an automated criminal supply chain.
The Three Gaps That Make You Vulnerable Right Now
If you are a small business owner reading this, there are three specific gaps that attackers exploit most frequently. Audit your own environment against each one:
Gap 1: Unpatched Endpoints and Network Devices
Every unpatched router, firewall, Windows machine, or NAS device on your network is a potential entry point. Attackers use publicly available databases of known vulnerabilities to scan the internet for easy targets. If your firewall is running three-year-old firmware, you are likely already listed in one of those databases.
The fix: Establish a regular patch cadence. Every endpoint and network device should be updated on a documented schedule—not "when someone remembers."
Gap 2: No Multi-Factor Authentication (MFA) on Critical Systems
Stolen credentials are the most common initial access vector after phishing. If your Microsoft 365 accounts, your remote access tools (VPN, RDP), or your cloud portals do not require multi-factor authentication, a stolen password is all an attacker needs.
The fix: Enable MFA universally—no exceptions, no opt-outs. This single control blocks over 99.9% of account compromise attacks, per Microsoft's own data.
Gap 3: Endpoint Security That's Stuck in 2010
Traditional antivirus software operates on a signature database—it can only block threats it already knows about. Modern ransomware variants are frequently modified to evade these signatures. By the time your antivirus database is updated, the attack has already succeeded.
The fix: Deploy Endpoint Detection and Response (EDR) software. EDR solutions like SentinelOne—which eSmith IT includes in our managed plans—use behavioral AI to detect and stop ransomware based on what it does, not just what it looks like. SentinelOne's 1-Click Rollback capability can undo the effects of a ransomware attack, restoring encrypted files to their pre-attack state.
What a Layered Defense Looks Like for a Small Business
Effective ransomware protection is not a single product purchase. It is a layered architecture where each layer compensates for the limitations of the others. Here is what a properly protected small business environment looks like:
- Next-generation EDR on every endpoint — SentinelOne or equivalent, actively monitored, not just installed and forgotten.
- MFA enforced across all accounts — Microsoft 365, email, VPN, remote access, cloud portals.
- Properly segmented network — your guest Wi-Fi should not share a broadcast domain with your server.
- Regular, immutable, offsite backups — tested quarterly so you know they actually work when needed.
- Patched and maintained network infrastructure — firewalls, switches, and routers running current firmware.
- Employee security awareness training — not a one-time onboarding slide deck, but recurring simulated phishing and training modules.
- A documented incident response plan — who do you call at 2:00 a.m. when something goes wrong?
None of these steps individually guarantees safety. Together, they create the depth of defense that makes your business a hard enough target that automated scanning tools move on to someone easier.
The Cost of Doing Nothing
The $200,000 average cost of a ransomware attack on an SMB sounds abstract until you consider what it actually covers:
- Downtime: The average ransomware recovery takes 21 days from attack to full restoration. For most small businesses, three weeks of disrupted operations is an existential event.
- Recovery costs: Forensics, data restoration, system rebuilding, and possible ransom payments.
- Reputational damage: Clients whose data was exposed will need to be notified—and many won't return.
- Regulatory exposure: If you handle healthcare data, financial records, or payment card information, a breach triggers notification obligations and potential fines.
- Cyber insurance claims: Premiums have risen dramatically for businesses without documented security controls. Some carriers are now denying claims outright if MFA was not enforced.
Compare those costs to a managed IT and security service at a fraction of that figure per year—and the decision becomes clear.
eSmith IT Protects Small Businesses Across the Carolinas
At eSmith IT, we specialize in exactly this kind of problem—building enterprise-grade security programs for businesses that don't have enterprise resources. We manage the complexity so you don't have to.
Our managed IT plans include:
- SentinelOne EDR deployed and actively monitored on every endpoint
- Microsoft 365 security policy management including MFA enforcement and Conditional Access
- Immutable cloud backup with Axcient for rapid, ransomware-proof recovery
- 24/7 alert monitoring so threats are caught before they become disasters
- Employee security training and simulated phishing campaigns
- Incident response support so you're never facing an attack alone
If you're not sure where your business stands, the first step is a cybersecurity assessment. We'll identify the specific gaps that put you at risk and give you a clear, prioritized roadmap to close them—without unnecessary complexity or cost.
Contact eSmith IT today to schedule your assessment and stop being an easy target.
About the Author
Kevin Smith
With over 25 years of verifiable IT experience across the Carolinas, Kevin Smith is an industry-recognized expert in Microsoft Cloud deployment, disaster recovery, and HIPAA compliance. As the President of eSmith IT Consulting, establishing secure enterprise infrastructure isn't just theory—it's his daily practice.