
Security Awareness Training: Why Your Employees Are Your Biggest Cyber Risk
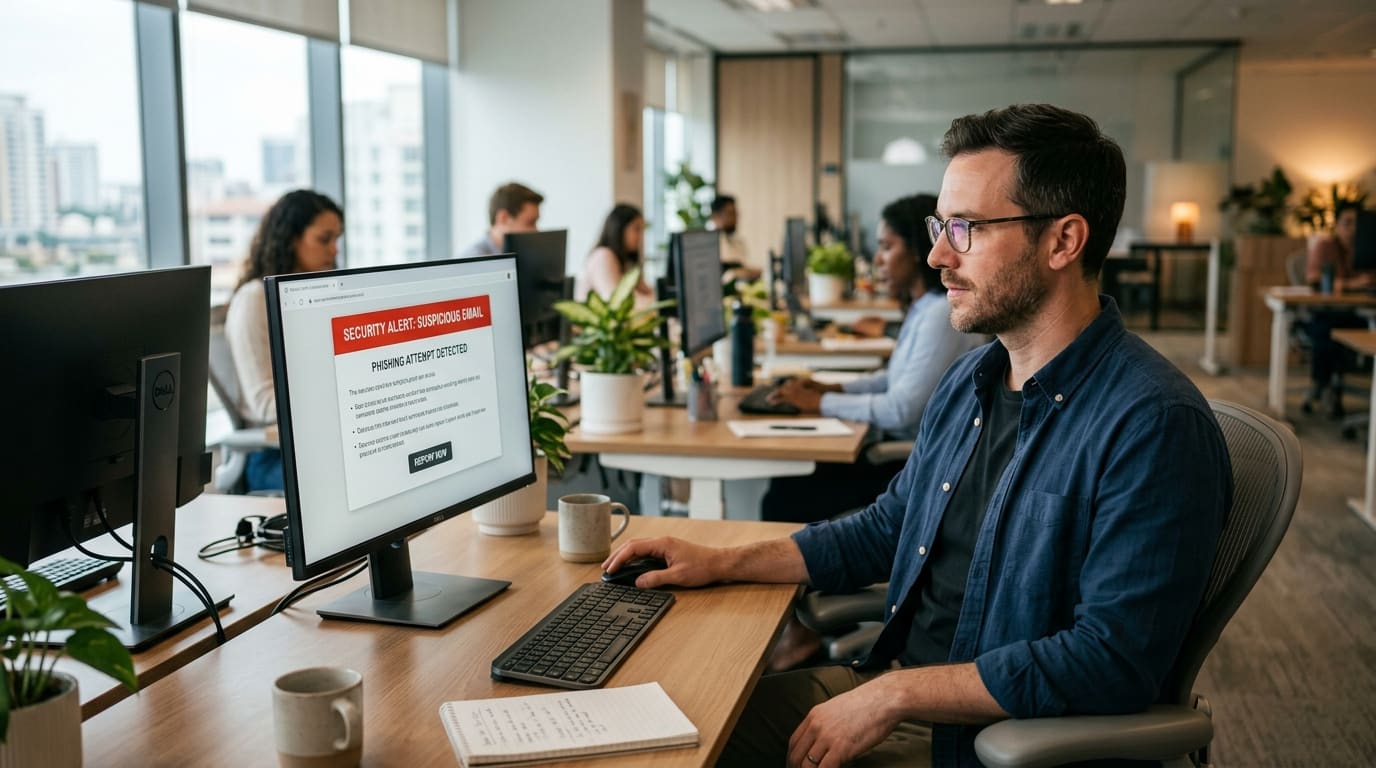
No firewall stops an employee who hands over their password. Security awareness training is the missing layer in most small business cyber defenses—here's what it is and why it matters.
You can have a next-generation firewall, enterprise EDR on every endpoint, and enforced multi-factor authentication across your entire organization. None of it matters if an employee clicks a convincing phishing link and types in their Microsoft 365 password.
That is not a hypothetical. According to Verizon's 2025 Data Breach Investigations Report, 68% of breaches involve a human element—an employee who was phished, who reused a compromised password, or who was socially engineered into granting access they shouldn't have. The technology layer of your security posture is only as strong as the humans operating within it.
Security Awareness Training (SAT) is how you close that gap. And for most Charlotte small businesses, it's the piece of the security stack that's missing entirely.
What Security Awareness Training Actually Is
Security Awareness Training is an ongoing program—not a one-time event—that teaches employees to recognize, avoid, and report cyber threats they encounter in their daily work. A well-run SAT program has three components working together:
1. Monthly Training Modules
Short, focused video lessons or interactive modules delivered to every employee on a regular cadence—typically monthly. Topics rotate through the threat landscape:
- Recognizing phishing and spear-phishing emails
- Spotting social engineering tactics (pretexting, urgency manipulation, authority impersonation)
- Safe password habits and the risk of credential reuse
- What to do when something looks suspicious
- Physical security basics (tailgating, unlocked screens, printed documents)
- Safe use of personal devices and public Wi-Fi
The key word is ongoing. A one-time annual compliance training video that employees click through in eight minutes is largely useless. Research from the SANS Institute shows that security awareness begins to decay within 90 days without reinforcement. Monthly touchpoints keep threat recognition sharp.
2. Simulated Phishing Campaigns
This is the component that separates effective SAT programs from checkbox exercises. Your IT partner or MSP sends realistic, fake phishing emails to your employees—impersonating known brands, internal IT requests, payroll notifications, shipping alerts, or even messages appearing to come from leadership.
Employees who click the simulated link don't get infected with anything. Instead, they immediately receive a brief teachable moment explaining what gave the email away and what they should have done differently. Their click is logged.
Over time, this produces a measurable metric: your organization's phish-prone percentage—the share of employees who would click a real attack under current conditions. The industry average for untrained employees hovers around 32–34% according to KnowBe4's 2025 Phishing by Industry Benchmarking Report. After 12 months of consistent SAT and simulated phishing, that number typically drops to under 5%.
That is a meaningful, quantifiable reduction in your organization's human attack surface.
3. Reporting Culture
The third piece—often overlooked—is building a culture where employees feel empowered to report suspicious emails, calls, or activity without fear of embarrassment. Many breaches persist longer than necessary because an employee who clicked something stays quiet rather than alerting IT.
An effective SAT program normalizes reporting. Employees learn that flagging a suspicious message is the right move whether or not it turns out to be a real threat, and that reporting quickly is the single most important thing they can do to limit damage if something does get through.
Why Employees Are the Primary Target
Attackers go after people because people are easier to compromise than properly configured technology. Consider what has changed in the past two years:
AI-generated phishing is now indistinguishable from legitimate email. The grammatical errors and awkward phrasing that used to signal a phishing attempt are gone. Generative AI allows attackers to craft hyper-personalized emails using scraped data from LinkedIn, your company website, and social media—matching the writing style of a known contact, referencing a real project, or mimicking a vendor your business actually uses. SlashNext reported a 4,151% increase in AI-crafted phishing attacks since ChatGPT's public release.
Vishing and deepfake audio are in active use against SMBs. Voice phishing calls using AI-cloned audio of a known executive or vendor contact are no longer limited to attacks on large enterprises. The technology is cheap, accessible, and increasingly deployed against smaller targets where defenses are thinner.
Business Email Compromise (BEC) doesn't need malware. BEC attacks—where an attacker convinces someone with financial authority to wire funds or change a vendor's bank account details—require zero technical exploitation. They require only a convincing email and an employee who hasn't been trained to verify out-of-band before acting. The FBI reported over $2.9 billion in BEC losses from small and mid-sized businesses in 2025 alone.
No endpoint security tool stops any of these attack vectors. They bypass technology entirely and go straight for the human.
What an Untrained Employee Actually Costs You
The financial exposure of a successful phishing attack ranges from painful to catastrophic depending on what the attacker can access once they have a foothold.
- Compromised Microsoft 365 account: An attacker with access to one employee's email can monitor communications silently for weeks, intercept wire transfer confirmations, reset passwords for connected SaaS tools, and pivot to other accounts within your organization.
- Credential-stuffing cascade: If the compromised password is reused anywhere else—which it almost certainly is—the attacker now has access to banking portals, accounting software, or remote access tools.
- Ransomware deployment: Many ransomware incidents begin with a phished credential. The attacker uses it to gain network access, escalates privileges over days or weeks, then deploys ransomware when maximum damage can be achieved. The average cost of a ransomware recovery for an SMB exceeded $108,000 in 2025 according to Sophos.
- Regulatory exposure: If the compromised account had access to protected health information (HIPAA), financial records, or payment card data, the breach triggers reporting obligations, potential fines, and legal liability—regardless of how the attacker got in.
How SAT Fits Into a Layered Security Strategy
Security Awareness Training is not a replacement for technical controls—it is the human layer that makes those controls work as intended. Think of it this way:
| Layer | What It Stops | |---|---| | Email filtering (Defender, Proofpoint) | Known malicious links and attachments | | EDR (SentinelOne) | Malware that lands on an endpoint | | MFA + Conditional Access | Compromised credentials used from unmanaged devices | | Security Awareness Training | The employee handing over credentials in the first place |
Each layer catches what the others miss. SAT operates at the front of that chain—before a threat ever touches your technology stack.
A properly trained employee who receives a suspicious email pauses, reports it to IT, and does not click. That single behavior change eliminates the entire downstream risk chain: no credential compromise, no malware, no breach, no incident response, no recovery costs.
What a Good SAT Program Looks Like for a Charlotte SMB
For small and mid-sized businesses in the Charlotte area, a practical SAT program doesn't require a dedicated security team or enterprise budget. The key requirements are:
Automated delivery. Training modules should be assigned and tracked automatically—not dependent on someone manually distributing links every month. Modern SAT platforms handle enrollment, assignment, completion tracking, and escalation for employees who fall behind.
Realistic simulated phishing. The phishing simulations should reflect actual current attack templates—not obviously fake emails that only the most careless employee would click. Platforms like KnowBe4 maintain libraries of thousands of real-world phishing templates updated continuously as new campaigns emerge.
Measurable outcomes. Your phish-prone percentage should be tracked over time. A good MSP will show you where your organization started, how it's trending month over month, and which departments or individuals represent the highest risk.
Completion accountability. Employees who don't complete training should be escalated—to their manager if necessary. SAT that isn't completed by the people who need it most provides no protection.
Appropriate scope. Every person with access to company email, systems, or data should be in the program. That includes part-time employees, contractors, and remote workers. Attackers don't limit their phishing to full-time staff.
How eSmith IT Delivers Security Awareness Training
At eSmith IT, Security Awareness Training is available as part of our managed security stack for small and mid-sized businesses throughout Charlotte, Huntersville, Mooresville, Concord, Cornelius, and Gastonia.
We handle the program end to end:
- Platform setup and employee enrollment — we configure the SAT platform, import your employee list, and handle onboarding so your team doesn't have to manage it
- Monthly training module assignment — curated, relevant content delivered automatically to every enrolled user on schedule
- Simulated phishing campaigns — realistic, regularly rotated phishing tests with immediate teachable moment delivery for employees who click
- Phish-prone percentage tracking — monthly reporting showing your organization's human risk score and trend over time
- Manager escalation — employees who skip training or repeatedly click simulations are flagged for follow-up
- Integration with your overall security posture — SAT sits alongside SentinelOne EDR, enforced MFA, email filtering, and backup in a coordinated defense
The goal isn't to catch employees doing something wrong. It's to build the kind of organizational reflexes where suspicious emails get reported, unusual requests get verified, and the human layer of your security posture is as strong as the technical one.
The Bottom Line
Attackers are not trying to outmaneuver your firewall. They are sending emails to your employees. For the cost of a single helpdesk ticket per user per month, a Security Awareness Training program systematically reduces the likelihood that any one of those emails becomes a breach.
For businesses that have invested in good technology controls and haven't addressed the human layer yet, SAT is often the highest-impact security improvement available.
If you're a small business in the Charlotte area and your team hasn't gone through structured security awareness training—or if the last time they did was a one-time video a few years ago—contact eSmith IT for a free security assessment. We'll evaluate your current human risk exposure and show you exactly what a managed SAT program would look like for your organization.
The most expensive phishing click is always the next one. Let's make sure it doesn't happen.
About the Author
Kevin Smith
With over 25 years of verifiable IT experience across the Carolinas, Kevin Smith is an industry-recognized expert in Microsoft Cloud deployment, disaster recovery, and HIPAA compliance. As the President of eSmith IT Consulting, establishing secure enterprise infrastructure isn't just theory—it's his daily practice.