
How to Secure Remote Employees for Small Businesses in 2026
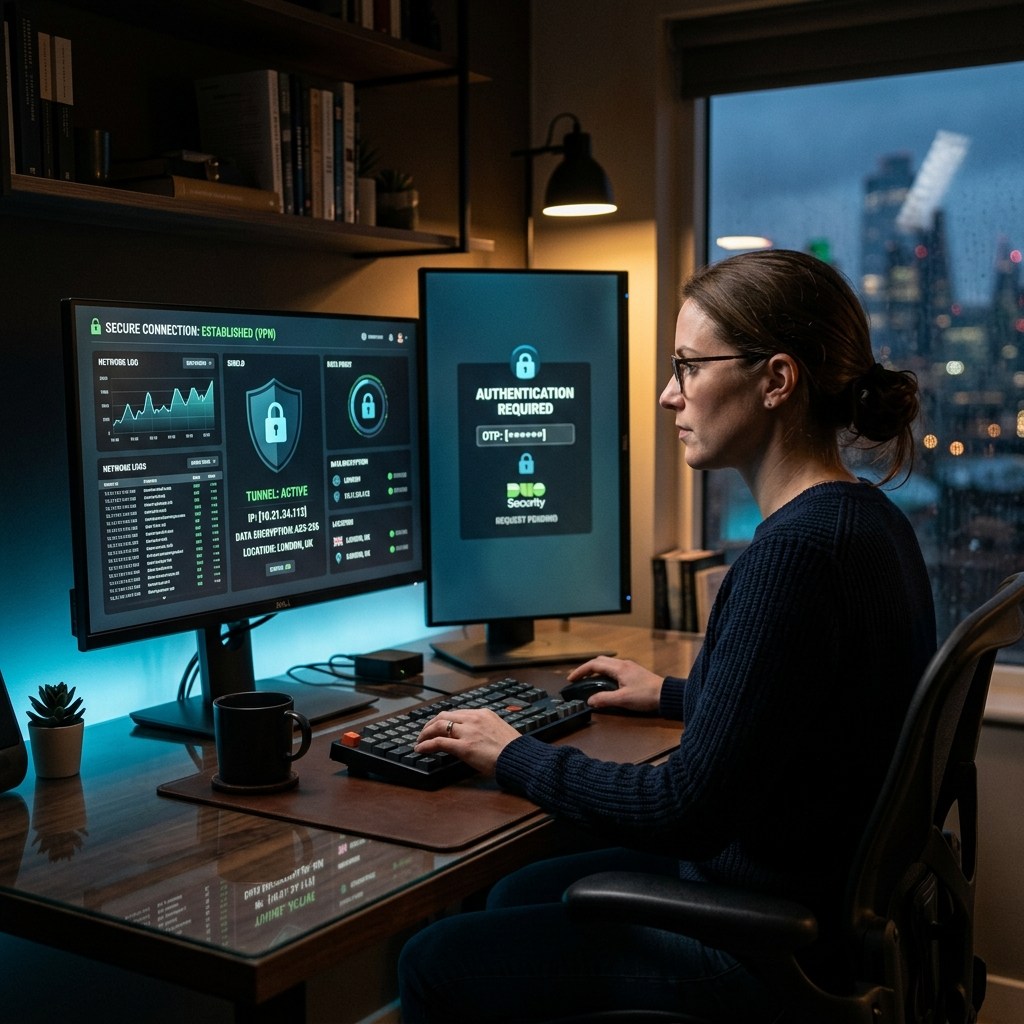
Home Wi-Fi networks are a hacker's dream. Here is how small businesses can properly secure remote and hybrid workers with business-grade VPNs, MFA, and MDM.
Hybrid work is here to stay. According to a 2025 Stanford study, nearly 29% of all paid workdays in the United States are now performed remotely—and for small businesses, that number is often higher because lean teams rely on flexible schedules to compete for talent.
The problem is that most small businesses secured their remote workforce with the same tool they would use for a personal Netflix subscription: a consumer VPN downloaded from an app store ad. Meanwhile, employees are connecting to business systems from home routers with factory-default passwords, family members' devices sharing the same subnet, and no visibility into what is actually traversing the network.
Home Wi-Fi networks are a hacker's dream. They are under-patched, under-monitored, and increasingly targeted. This guide explains what a proper remote workforce security posture looks like for a small business in 2026—and why the tools most businesses rely on today are leaving them dangerously exposed.
Why Consumer VPNs Aren't Enough for Business Data
Consumer VPN products—NordVPN, ExpressVPN, Surfshark, and their competitors—were designed to protect individual internet privacy. They encrypt traffic between a single device and the VPN provider's servers, masking your IP address and preventing your ISP from logging your browsing. That is a useful privacy tool for individuals. It is not a business security solution.
Here is what consumer VPNs do not provide:
- Centralized policy management: An IT team or MSP cannot enforce connection requirements, monitor usage, or audit which employees are connected and when. Every user manages their own credentials and settings independently.
- Split tunneling control: Consumer VPNs either route all traffic or none of it through the tunnel, with no ability to enforce that business applications always traverse the VPN while personal traffic goes direct.
- Integration with your business identity layer: Consumer VPNs have no awareness of your Microsoft 365 tenant, your Active Directory, or your Conditional Access policies. They cannot enforce that only compliant, managed devices connect to your internal resources.
- Zero Trust Network Access (ZTNA): Modern business security is built on the principle of "never trust, always verify"—authenticating device health, user identity, and access scope on every session. Consumer VPNs authenticate only to the VPN provider, not to your business.
- Audit logging: When a security incident occurs, you need logs. Who connected? From which IP? At what time? To which resources? Consumer VPNs provide none of this for business owners or IT teams.
What business VPN setup actually looks like
A proper business VPN for small companies in 2026 is typically a business-grade solution such as Cisco Meraki Client VPN, Fortinet FortiClient, or a ZTNA platform like Cloudflare Access or Microsoft Entra Private Access. These solutions:
- Require enrollment of managed devices before connection is permitted
- Enforce MFA as a condition of VPN authentication
- Log all sessions with user identity, device, IP, and timestamp
- Integrate with your existing identity provider (Microsoft Entra ID / Azure AD)
- Support granular access policies—a remote sales rep only reaches CRM, not the file server
The cost difference between a consumer VPN subscription and a proper business VPN is often less than $10 per user per month. The security difference is enormous.
Setting Up Multi-Factor Authentication (MFA) the Right Way
Multi-factor authentication is the single highest-impact security control you can implement for a remote workforce. According to Microsoft's own telemetry, MFA blocks over 99.9% of account compromise attacks. And yet, in 2025, Verizon's Data Breach Investigations Report found that a significant portion of breaches at small businesses still involved valid credentials with no second factor required.
Implementing MFA "the right way" means more than just turning on text message codes. Here is what a proper MFA deployment looks like:
Step 1: Enforce MFA on every business account
This means Microsoft 365, your VPN, your line-of-business software, your accounting platform, and any cloud service that holds business data. Use Conditional Access policies in Microsoft Entra ID (formerly Azure AD) to enforce this at the identity layer—not just at the application layer—so it cannot be bypassed.
Step 2: Move away from SMS-based MFA where possible
SMS authentication codes are vulnerable to SIM-swapping attacks, where an attacker convinces your carrier to transfer your phone number to their device. For business accounts, use:
- Microsoft Authenticator app with number matching (resistant to push bombing attacks)
- FIDO2 security keys (YubiKey, Feitian) for your highest-privilege accounts
- Certificate-based authentication for device-level trust
Step 3: Configure MFA fatigue protections
"MFA fatigue" or "push bombing" is an attack where a criminal who already has your password sends dozens of MFA push requests until an exhausted user taps Approve just to make it stop. Microsoft Authenticator's number matching feature defeats this by requiring the user to type a number displayed on the login screen into the app—a simple but highly effective control.
Step 4: Protect privileged accounts with the most friction
Your domain administrator, your Microsoft 365 global admin, your backup administrator—these accounts should have the highest MFA friction, including phishing-resistant FIDO2 keys, and should ideally be break-glass accounts used only when absolutely necessary. Regular daily work should never happen from a global admin account.
Step 5: Train employees before you roll out enforcement
A surprise MFA enforcement without employee training generates help desk calls, frustration, and workarounds. A brief walkthrough—"here is the app, here is how enrollment works, here is why we are doing this"—dramatically improves adoption and reduces friction at rollout.
Mobile Device Management (MDM) for Personal Laptops
This is the hardest conversation in small business security: employees are connecting to your business systems from personal devices that your IT team has never touched, cannot see, and cannot control.
A personal laptop has no guarantee of current patches, no endpoint detection and response (EDR) software, no enforced disk encryption, and no ability to be remotely wiped if it is lost or stolen. From a security standpoint, it is an unmanaged endpoint—and unmanaged endpoints are one of the most common entry points for breaches involving remote workers.
Mobile Device Management (MDM) solves this. For small businesses in 2026, the two primary approaches are:
Full device management (MDM)
The device is enrolled into Microsoft Intune or a comparable MDM platform. IT can enforce:
- Disk encryption (BitLocker on Windows, FileVault on Mac)
- OS and application patch compliance—devices that are not current on patches lose access
- Screen lock and PIN requirements
- Remote wipe in the event of loss or theft
- EDR agent enrollment (SentinelOne, CrowdStrike Falcon Go)
This approach works best for company-owned devices. For personal devices (BYOD), it can feel intrusive to employees who are concerned about employer visibility into their personal files and activity.
Mobile Application Management (MAM) — the BYOD-friendly approach
MAM manages the business applications on a personal device without enrolling the device itself. With Microsoft Intune's MAM policies, you can:
- Require PIN or biometric authentication to open business apps
- Prevent copy/paste of business data out of managed apps into personal apps
- Block screenshots from within business applications
- Remotely wipe only business data, leaving personal data untouched
- Enforce encryption of business data at rest on the device
MAM is the right balance for small businesses with a BYOD culture. Employees retain privacy over their personal phone and laptop content; you retain control over the business data those devices access.
Conditional Access as the enforcement layer
Whether you use full MDM or MAM, the key is to connect your device management platform to your Conditional Access policies in Microsoft Entra ID. This creates a policy that says: "Business resources are only accessible from devices that are enrolled and compliant." A personal device that has not been enrolled, or that has fallen out of compliance (missed patches, disabled encryption), cannot reach email, SharePoint, or your internal systems—even with valid credentials and MFA.
This is the architecture that closes the gap. Valid credentials plus MFA plus a compliant, managed device equals access. Anything missing from that chain equals a blocked request.
Building a Secure Remote Work Posture: The Complete Picture
A properly secured remote workforce for a small business in 2026 looks like this:
- Business-grade VPN or ZTNA: Cisco Meraki, Fortinet, or Cloudflare Access replacing consumer VPNs
- Enforced MFA with phishing-resistant methods: Microsoft Authenticator with number matching at minimum; FIDO2 keys for privileged accounts
- Device management: Intune MDM for company devices, MAM policies for BYOD
- EDR on every endpoint: SentinelOne or CrowdStrike deployed and reporting to a monitored console
- Conditional Access policies: Tying identity, device compliance, and MFA together as conditions of access
- Security awareness training: Quarterly simulated phishing and remote security best practices
- Patch management: Automated patching that closes critical vulnerabilities within 48 hours across all managed endpoints
None of these controls is especially exotic. They are not reserved for enterprises. They are the baseline that every small business with remote employees needs to operate safely in 2026.
How eSmith IT Helps Charlotte Small Businesses Secure Remote Workers
Designing and maintaining this architecture is not a one-afternoon project. It requires expertise across identity management, network security, endpoint management, and policy configuration—and it requires ongoing monitoring to catch and respond to the events that even great controls cannot prevent.
eSmith IT provides fully managed remote workforce security for small and mid-sized businesses throughout the Charlotte metro area, including Huntersville, Mooresville, Cornelius, Concord, and Gastonia. Our Managed IT Services Charlotte NC include business VPN configuration, Microsoft Intune MDM/MAM deployment, Conditional Access policy design, SentinelOne EDR management, and 24/7 monitoring—all for a flat monthly fee with no per-incident billing surprises.
If your employees are connecting to your business systems from home and you are not certain what security controls are in place, contact eSmith IT for a free remote security assessment. We will audit your current posture, identify the specific gaps in your remote access architecture, and give you a clear, prioritized plan to close them before they become a breach.
The question is not whether your remote workers represent a security exposure. In 2026, they almost certainly do. The question is whether you find out before or after an attacker does.
About the Author
Kevin Smith
With over 25 years of verifiable IT experience across the Carolinas, Kevin Smith is an industry-recognized expert in Microsoft Cloud deployment, disaster recovery, and HIPAA compliance. As the President of eSmith IT Consulting, establishing secure enterprise infrastructure isn't just theory—it's his daily practice.