
The 3 Essential Layers of Data Backup Every Business Needs
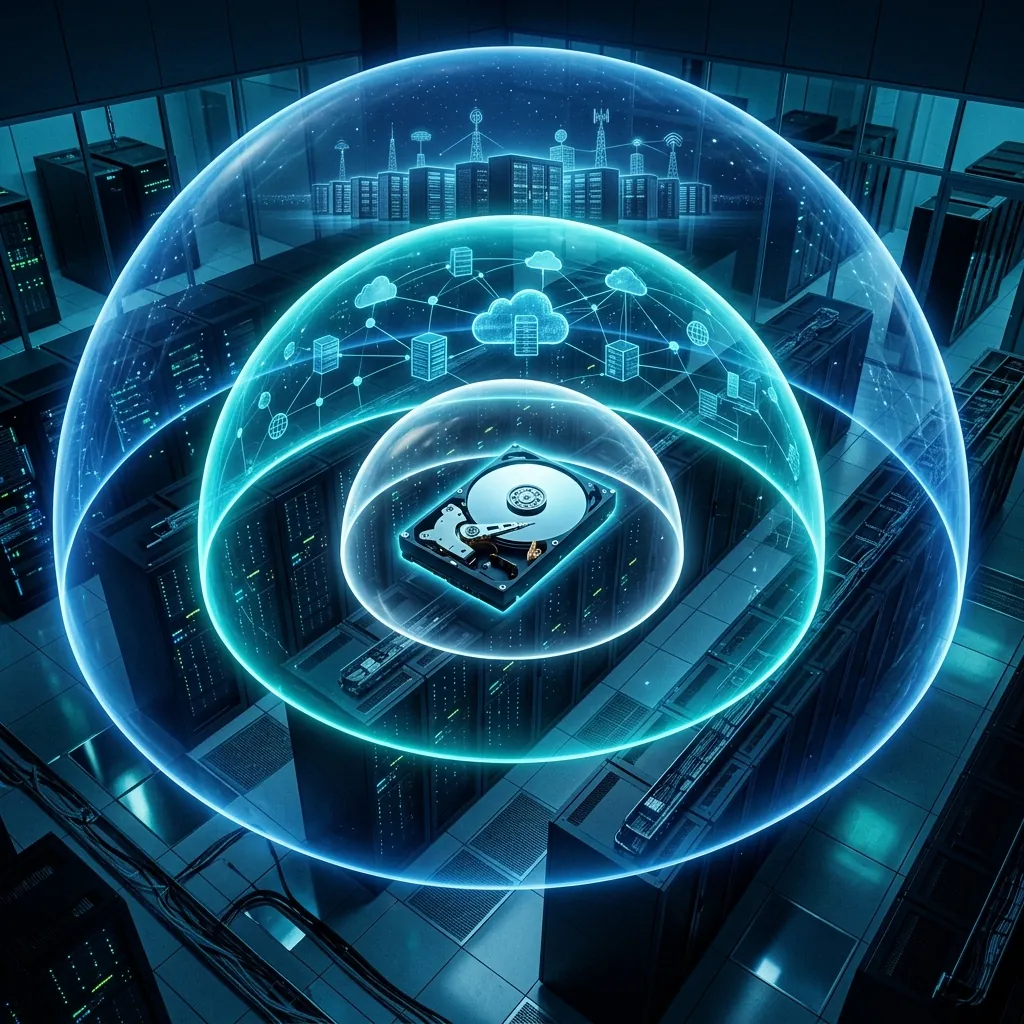
Google Drive and OneDrive are not backups. Learn the three distinct layers of data protection that actually keep your business running after a ransomware attack or hardware failure.
There is a conversation we have regularly with business owners in the Charlotte area, and it almost always starts the same way.
We ask: "Do you have a backup of your critical data?"
They say: "Yes, everything is in OneDrive," or "We sync everything to Google Drive."
And then we have to deliver some uncomfortable news: that is not a backup.
It is a synchronization tool. It is a collaboration platform. It is exceptionally good at those things. But when your server crashes, when ransomware encrypts your file shares, or when an employee permanently deletes the wrong folder — a sync tool replicates the disaster as faithfully as it replicated the original data.
This distinction matters enormously. According to the 2024 Veeam Data Protection Trends Report, 93% of ransomware attacks specifically target backup repositories, because attackers know that destroying your recovery options is just as effective as encrypting your active files. If your only "backup" is a cloud drive connected to the same accounts that were compromised, you have no backup at all.
The solution is a concept that IT professionals call layered data protection, and it can be summarized in three specific, non-negotiable tiers.
Why Sync Tools Like OneDrive and Google Drive Are Not Backups
Before explaining what a proper backup strategy looks like, it is worth being precise about why cloud sync tools fail as a recovery mechanism.
The Synchronization Problem
OneDrive, Google Drive, and Dropbox all work on the same fundamental principle: whatever is on your device is mirrored to the cloud, and whatever is in the cloud is mirrored back to your device. This is exactly what makes them useful for collaboration.
It is also exactly what makes them dangerous as a sole backup solution.
- Ransomware encrypts your local files. The sync client immediately pushes those encrypted, corrupted files to the cloud, overwriting the clean originals. Within minutes, both your local copy and your cloud copy are encrypted.
- An employee deletes a folder. That deletion syncs to every connected device and to every other user who has access. The files are gone from all locations simultaneously.
- A misconfigured permission change corrupts your SharePoint library. The corruption propagates instantly.
Most sync services do offer version history — typically 30 to 90 days for business plans. But version history has critical limitations: it is per-file, it can be exhausted by a mass encryption event that creates thousands of new file versions in seconds, and it is accessible to anyone who can access the account — including a compromised one.
This is not a criticism of these tools. OneDrive and Google Drive are excellent products being used outside their intended purpose when treated as a business backup strategy.
Layer 1: The Local Backup (Your Speed Layer)
The first layer of a proper backup architecture is a local, on-premises backup — meaning a copy of your data stored on a device that is physically on your premises or directly connected to your infrastructure, but isolated from your primary network.
What It Protects Against
- Hardware failure (server crash, drive failure)
- Accidental file deletion with rapid recovery
- Operating system corruption requiring full system restore
Why It Must Be Isolated
The critical word here is isolated. A backup drive plugged directly into your server and visible to the network is not a true local backup — it is just a secondary folder. Ransomware will encrypt it. An attacker with network access can delete it.
Effective local backup solutions like Veeam create image-level snapshots of your entire system — not just individual files — and store them in a way that is not directly accessible through standard file paths. They use proprietary repositories that ransomware cannot natively encrypt.
Recovery Time Advantage
The primary advantage of local backup is speed. Restoring a server from a local snapshot typically takes 2 to 4 hours. Restoring the same server from a cloud-only backup over an internet connection can take 24 to 72 hours depending on data volume and bandwidth. For a business where every hour of downtime has a real dollar cost, that difference is often the difference between a painful inconvenience and a catastrophic business disruption.
Key metric to know: This is what IT professionals call the Recovery Time Objective (RTO). Your local backup is what keeps your RTO measured in hours rather than days.
Layer 2: The Offsite or Cloud Backup (Your Resilience Layer)
The second layer is a geographically separate copy of your data — either in a managed cloud backup environment or a physically separate location.
What It Protects Against
- On-premises disasters (fire, flooding, theft, building power failure)
- Ransomware attacks that successfully compromise local backups
- Hardware failures that occur faster than local backups can run
The 3-2-1 Rule
This layer is where the foundational principle of enterprise data protection comes into focus: the 3-2-1 backup rule.
- 3 copies of your data
- On 2 different types of storage media
- With 1 copy stored offsite
Layers 1 and 2 together accomplish the 3-2-1 requirement. Local backup provides your on-premises copies on dedicated backup storage. Offsite/cloud backup provides the geographic separation.
What Makes a Cloud Backup Different From Cloud Sync
Unlike OneDrive or Google Drive, a dedicated cloud backup solution like Axcient or Veeam Cloud Connect operates independently of your active account credentials. This is the critical difference:
- Backup data is stored in an immutable format — once written, it cannot be modified or deleted, even by an administrator, for a defined retention period.
- The backup service authenticates separately from your Microsoft 365 or Google Workspace accounts, meaning a compromised account cannot access or delete the backups.
- Data is retained for weeks or months as point-in-time snapshots, allowing you to restore your environment to exactly how it was before a specific incident.
Immutability is not optional. A 2023 Sophos ransomware report found that in 96% of ransomware attacks where backups were targeted, the attackers attempted to encrypt or delete them. Immutable backups are the only reliable defense against this tactic.
Layer 3: The Tested Recovery Process (Your Confidence Layer)
This is the layer that almost every small business skips entirely — and it is arguably the most important one.
An untested backup is a hypothesis, not a safety net.
The Brutal Truth About Untested Backups
We have worked with businesses that believed they had reliable backups for years, only to discover during an actual recovery event that:
- The backup jobs had been silently failing for months due to a misconfigured credential
- The backup media had degraded and was no longer readable
- The backup existed but the recovery process took 3x longer than expected, causing extended downtime
- A critical database or application was excluded from the backup scope and was not recoverable
According to a 2023 Enterprise Strategy Group survey, only 46% of organizations had successfully tested their backup recovery process in the past 12 months. The implication for the other 54% is sobering.
What a Tested Recovery Process Looks Like
A proper backup validation program includes:
-
Monthly automated backup verification — Your backup platform should be confirming that backup jobs completed successfully, that the data is readable, and that checksum validation passes. This should generate a report you can review.
-
Quarterly recovery drills — At least once per quarter, an IT technician should perform an actual test restore of a representative workload — a server, a mailbox, or a critical file share — to a sandboxed environment. This verifies the entire chain: the backup data is intact, the recovery process works, and the timeframe matches your RTO targets.
-
Annual full disaster recovery simulation — Once per year, simulate a complete failure scenario. Can your business actually restore its most critical systems within the timeframe your operations require? This exercise consistently reveals gaps that no amount of theoretical planning will surface.
-
Documented recovery runbook — The recovery process should be written down in enough detail that someone other than your primary IT contact can execute it under pressure at 2:00 a.m. on a holiday weekend. Because that is frequently when disasters happen.
Why This Is a Layer, Not an Afterthought
The reason we call this a layer rather than a periodic maintenance task is that it represents an ongoing capability, not a one-time setup activity. Your backup infrastructure will drift — software updates, credential rotations, new systems added to scope, staff changes. The only way to know your recovery capability is still intact is to continuously validate it.
What a Complete Backup Architecture Looks Like in Practice
For a typical small-to-mid-sized business, a complete, properly layered backup system looks like this:
| Layer | Solution Example | What It Protects | Recovery Time | |---|---|---|---| | Layer 1: Local | Veeam | Hardware failure, rapid file recovery | 2–4 hours | | Layer 2: Offsite Cloud | Axcient / Veeam Cloud Connect | Ransomware, site disaster, account compromise | 4–24 hours | | Layer 3: Validation | Monthly reports + quarterly drills | Backup integrity, process reliability | N/A — enables Layers 1 & 2 |
This is not a luxury architecture reserved for enterprise companies. This is the baseline that every business handling customer data, financial records, or any operationally critical information should have in place.
The Google Drive and OneDrive Problem — A Final Word
To be absolutely clear: you should still use OneDrive and Google Drive. They are exceptional productivity tools, and disabling sync is not the answer.
The answer is understanding exactly what role they play. They are collaboration and productivity platforms. They provide convenience and accessibility. They offer limited version history as a convenience feature.
They are not — and were never designed to be — your disaster recovery solution.
The distinction is simple: if your entire building burned down tonight, could you restore your complete business operations from your current backup strategy? If the answer involves logging into OneDrive and hoping the files are there, you do not have a backup strategy. You have a sync account.
How eSmith IT Approaches Backup for Our Clients
Every business we take on as a managed IT client undergoes a backup assessment as part of onboarding. We document every system that requires protection, define the acceptable Recovery Time Objective and Recovery Point Objective (the maximum amount of data loss the business can absorb), and design a layered backup architecture that meets those requirements within a realistic budget.
For most of our clients, this includes:
- Veeam and Axcient for combined local and cloud backup with immutable storage and automated verification
- Microsoft 365 backup via Axcient, covering Exchange Online, SharePoint, OneDrive, and Teams — because Microsoft explicitly states that backing up your M365 data is your responsibility, not theirs
- Monthly backup health reports delivered directly to business owners, not buried in an IT ticket queue
- Quarterly recovery validation built into our maintenance schedule
We have used this architecture to help clients recover from ransomware attacks in hours rather than weeks, and we have used it to tell clients with confidence that their backup is working — because we test it regularly and we can prove it.
If you are not certain your backup strategy would actually work when you need it, that uncertainty is the problem. Contact eSmith IT for a backup assessment. We will tell you exactly where you stand — and exactly what it would take to give you the kind of recovery confidence your business deserves.
About the Author
Kevin Smith
With over 25 years of verifiable IT experience across the Carolinas, Kevin Smith is an industry-recognized expert in Microsoft Cloud deployment, disaster recovery, and HIPAA compliance. As the President of eSmith IT Consulting, establishing secure enterprise infrastructure isn't just theory—it's his daily practice.